sarah_francoise Articles

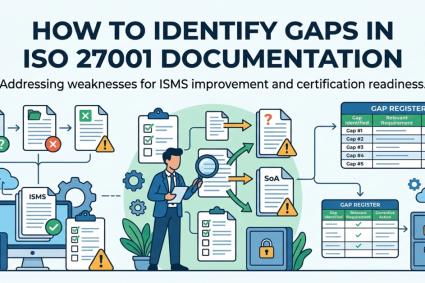
How to Identify Gaps in ISO 27001 Documentation

Discover how to identify ISO 27001 documentation gaps, review ISMS requirements, assess risk records and security controls, and implement corrective actions to strengthen information security, improve documentation accuracy, and prepare...
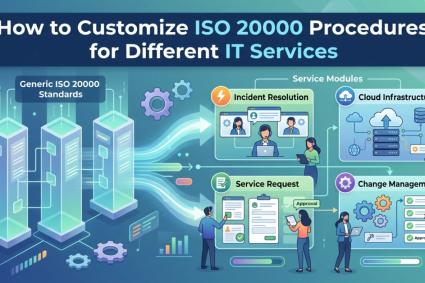
How to Customize ISO 20000 Procedures for Different IT Services

Learn how to customize ISO 20000 procedures for different IT services, including incident management, change control, and service requests. Discover practical strategies to define responsibilities, improve ITSM workflows, maintain documentation,...

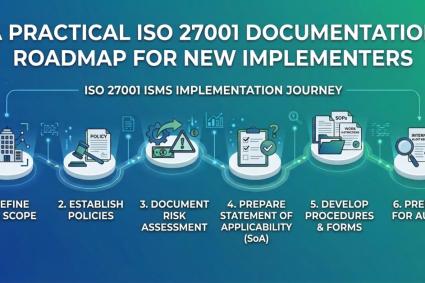
A Practical ISO 27001 Documentation Roadmap for New Implementers

Learn a practical ISO 27001 documentation roadmap covering ISMS scope, security policies, risk assessment, Statement of Applicability, procedures, records, and audit preparation to support effective ISMS implementation and certification readiness.

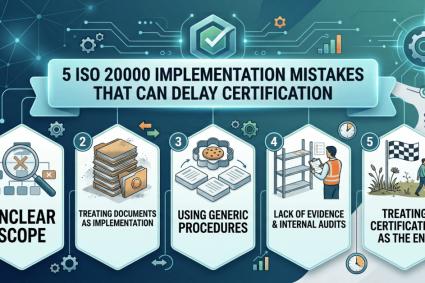
5 ISO 20000 Implementation Mistakes That Can Delay Certification

Learn the 5 common ISO 20000 implementation mistakes that can delay certification, including unclear scope, generic documentation, weak evidence, poor internal audits, and limited continual improvement.

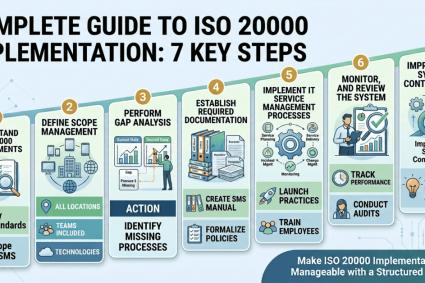
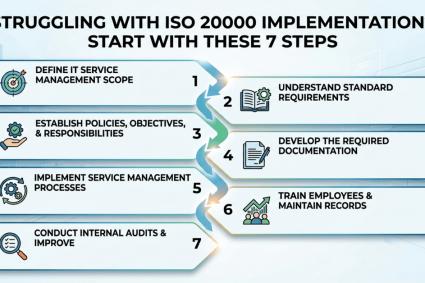
Struggling With ISO 20000 Implementation? Start With These 7 Steps

Discover seven practical steps for ISO 20000 implementation, including understanding requirements, defining IT service scope, conducting gap analysis, developing documentation, implementing processes, auditing the SMS, and driving continual improvement.

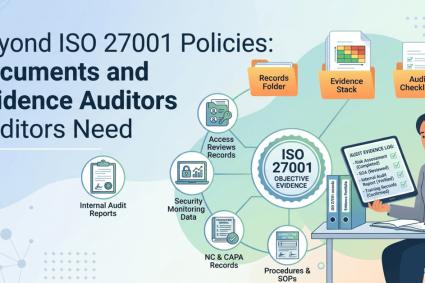
Beyond ISO 27001 Policies: What Documents and Evidence Do Auditors...

Learn what ISO 27001 auditors need beyond information security policies. This article explains the essential ISMS documents, Statement of Applicability (SoA), risk assessments, procedures, records, and objective evidence required for...

Struggling With ISO 20000 Implementation? Start With These 7 Steps

Discover 7 practical steps for ISO 20000 implementation, including scope definition, gap analysis, documentation, process implementation, employee training, internal audits, and continual improvement.

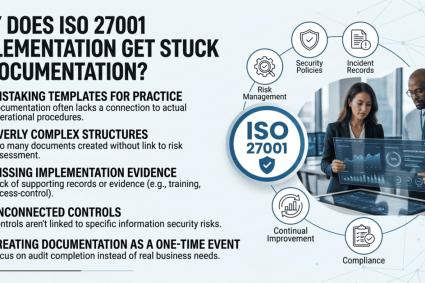
Why Do ISO 27001 Implementations Get Stuck at the Documentation...

Many ISO 27001 implementations stall because documentation is disconnected from real processes. Learn how structured ISO 27001 documents, risk assessment, procedures, and audit records create an effective ISMS and support...

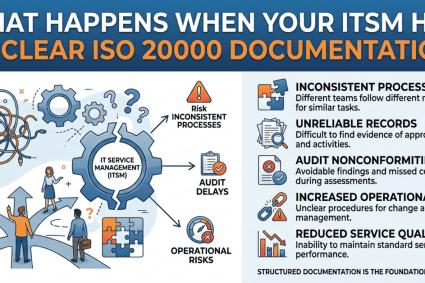
What Happens When Your ITSM Has No Clear ISO 20000...

Poor ISO 20000 documentation can lead to inconsistent IT service processes, audit delays, and certification challenges. Learn why structured ITSMS documentation is essential for compliance, operational control, and continual service...

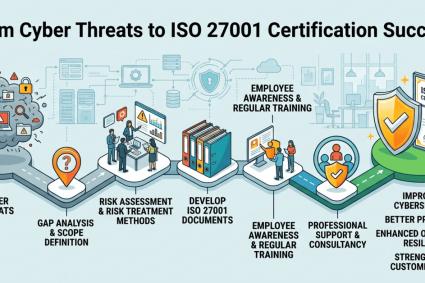
From Cyber Threats to ISO 27001 Certification Success: A Practical...

Learn how ISO 27001 certification helps organizations combat cyber threats through a structured ISMS, effective risk management, robust security controls, and continual improvement to protect sensitive information and strengthen business...